

remote-address, you can use it for a configured point-to-point link between two routers. This routes IPv6 traffic; it does not bridge Ethernet or automatically provide public IPv6 Internet access.
This example uses private IPv6 networks behind two routers and RouterOS’s ipsec-secret option. See the MikroTik interface reference for current behavior and IPsec defaults.
Before you begin
- You administer both RouterOS routers and their firewall policies.
- Both ends have reachable public IPv4 addresses. This example does not cover NAT.
- Each router has an appropriate LAN interface or bridge for its downstream network. Do not blindly apply the LAN address to a VPS’s public/WAN interface.
- Back up the router configuration and keep an alternate management connection available.
Example address plan
All addresses below are documentation examples. Replace the IPv4 endpoints with your actual public addresses. For production private networks, generate a unique ULA/48 prefix and allocate non-overlapping subnets; see RFC 4193.
The ULA addresses are for private communication, not globally routed Internet addresses. Replace
LAN_INTERFACE below with each router’s actual downstream interface or bridge.
1. Enable IPv6
On both routers: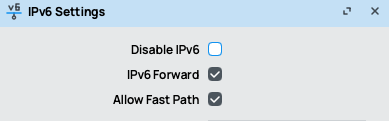
2. Create the tunnel
Use the same long, randomly generated secret at both ends.REPLACE_WITH_UNIQUE_SECRET is a placeholder, not a usable example password. Do not reuse a public documentation password.
On Router 1:
ipsec-secret creates a dynamic IPsec peer and policy. Review the negotiated algorithms and policy against your requirements; creating the interface alone does not prove that encrypted traffic is flowing.
3. Assign the tunnel and LAN addresses
On Router 1:4. Route the remote LAN
On Router 1:5. Verify both routing and encryption
First check that the expected IPsec peer and security associations are established in RouterOS. Then test the remote tunnel endpoint and remote LAN router address. From Router 1:1280 may also need path-specific investigation; it is not a guarantee that every underlying path can carry the encapsulated packet without fragmentation.